Ben Dechrai
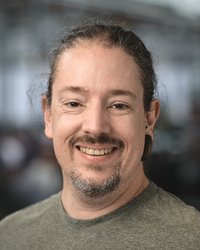
Ben has spent more than 20 years helping companies improve how they build software, more recently the practical side of agentic engineering: getting tools like Claude Code to deliver production-quality work rather than demos, and structuring repos, prompts and workflows so the output is effective, resilient and secure. That rests on decades of building and shipping product in application security and identity. He is a Microsoft MVP and has given 100+ talks on six continents, including DEF CON.
Sessions Montréal 2027
Teach Your Agent to Forget
Session en Anglais - Débutant
Your agent finally remembers things. Congratulations, it is now a data leak with a personality. The whole room gets a link to one agent and your job is to ruin it: feed it lies, leak someone else's context, make it hold a grudge. We watch its memory fill up, then fix each failure with boring, fast tools: streams, structured records, vector search and expiry. You leave knowing what an agent must forget, and why that is where production breaks.
Ten Key Steps for Enhanced Web App Security
Session en Anglais - Débutant
Knowing the OWASP Top 10 does not tell you where to start on a codebase with no security headers, unvalidated input and CORS set to *. This is the prioritised checklist I wish I had: ten steps from preventing common vulnerabilities and hardening authentication to CI/CD security and DDoS defence, with live demos of the attacks and the fixes in real code, ordered by impact for effort, so you leave with a plan for Monday morning.
Sessions Montréal 2026
- Building Rock-Solid Encrypted Applications
- Rogue LLMs: Securing Prompts and Ensuring Persona Fidelity